Understand the different user roles in Kuviq.
Overview
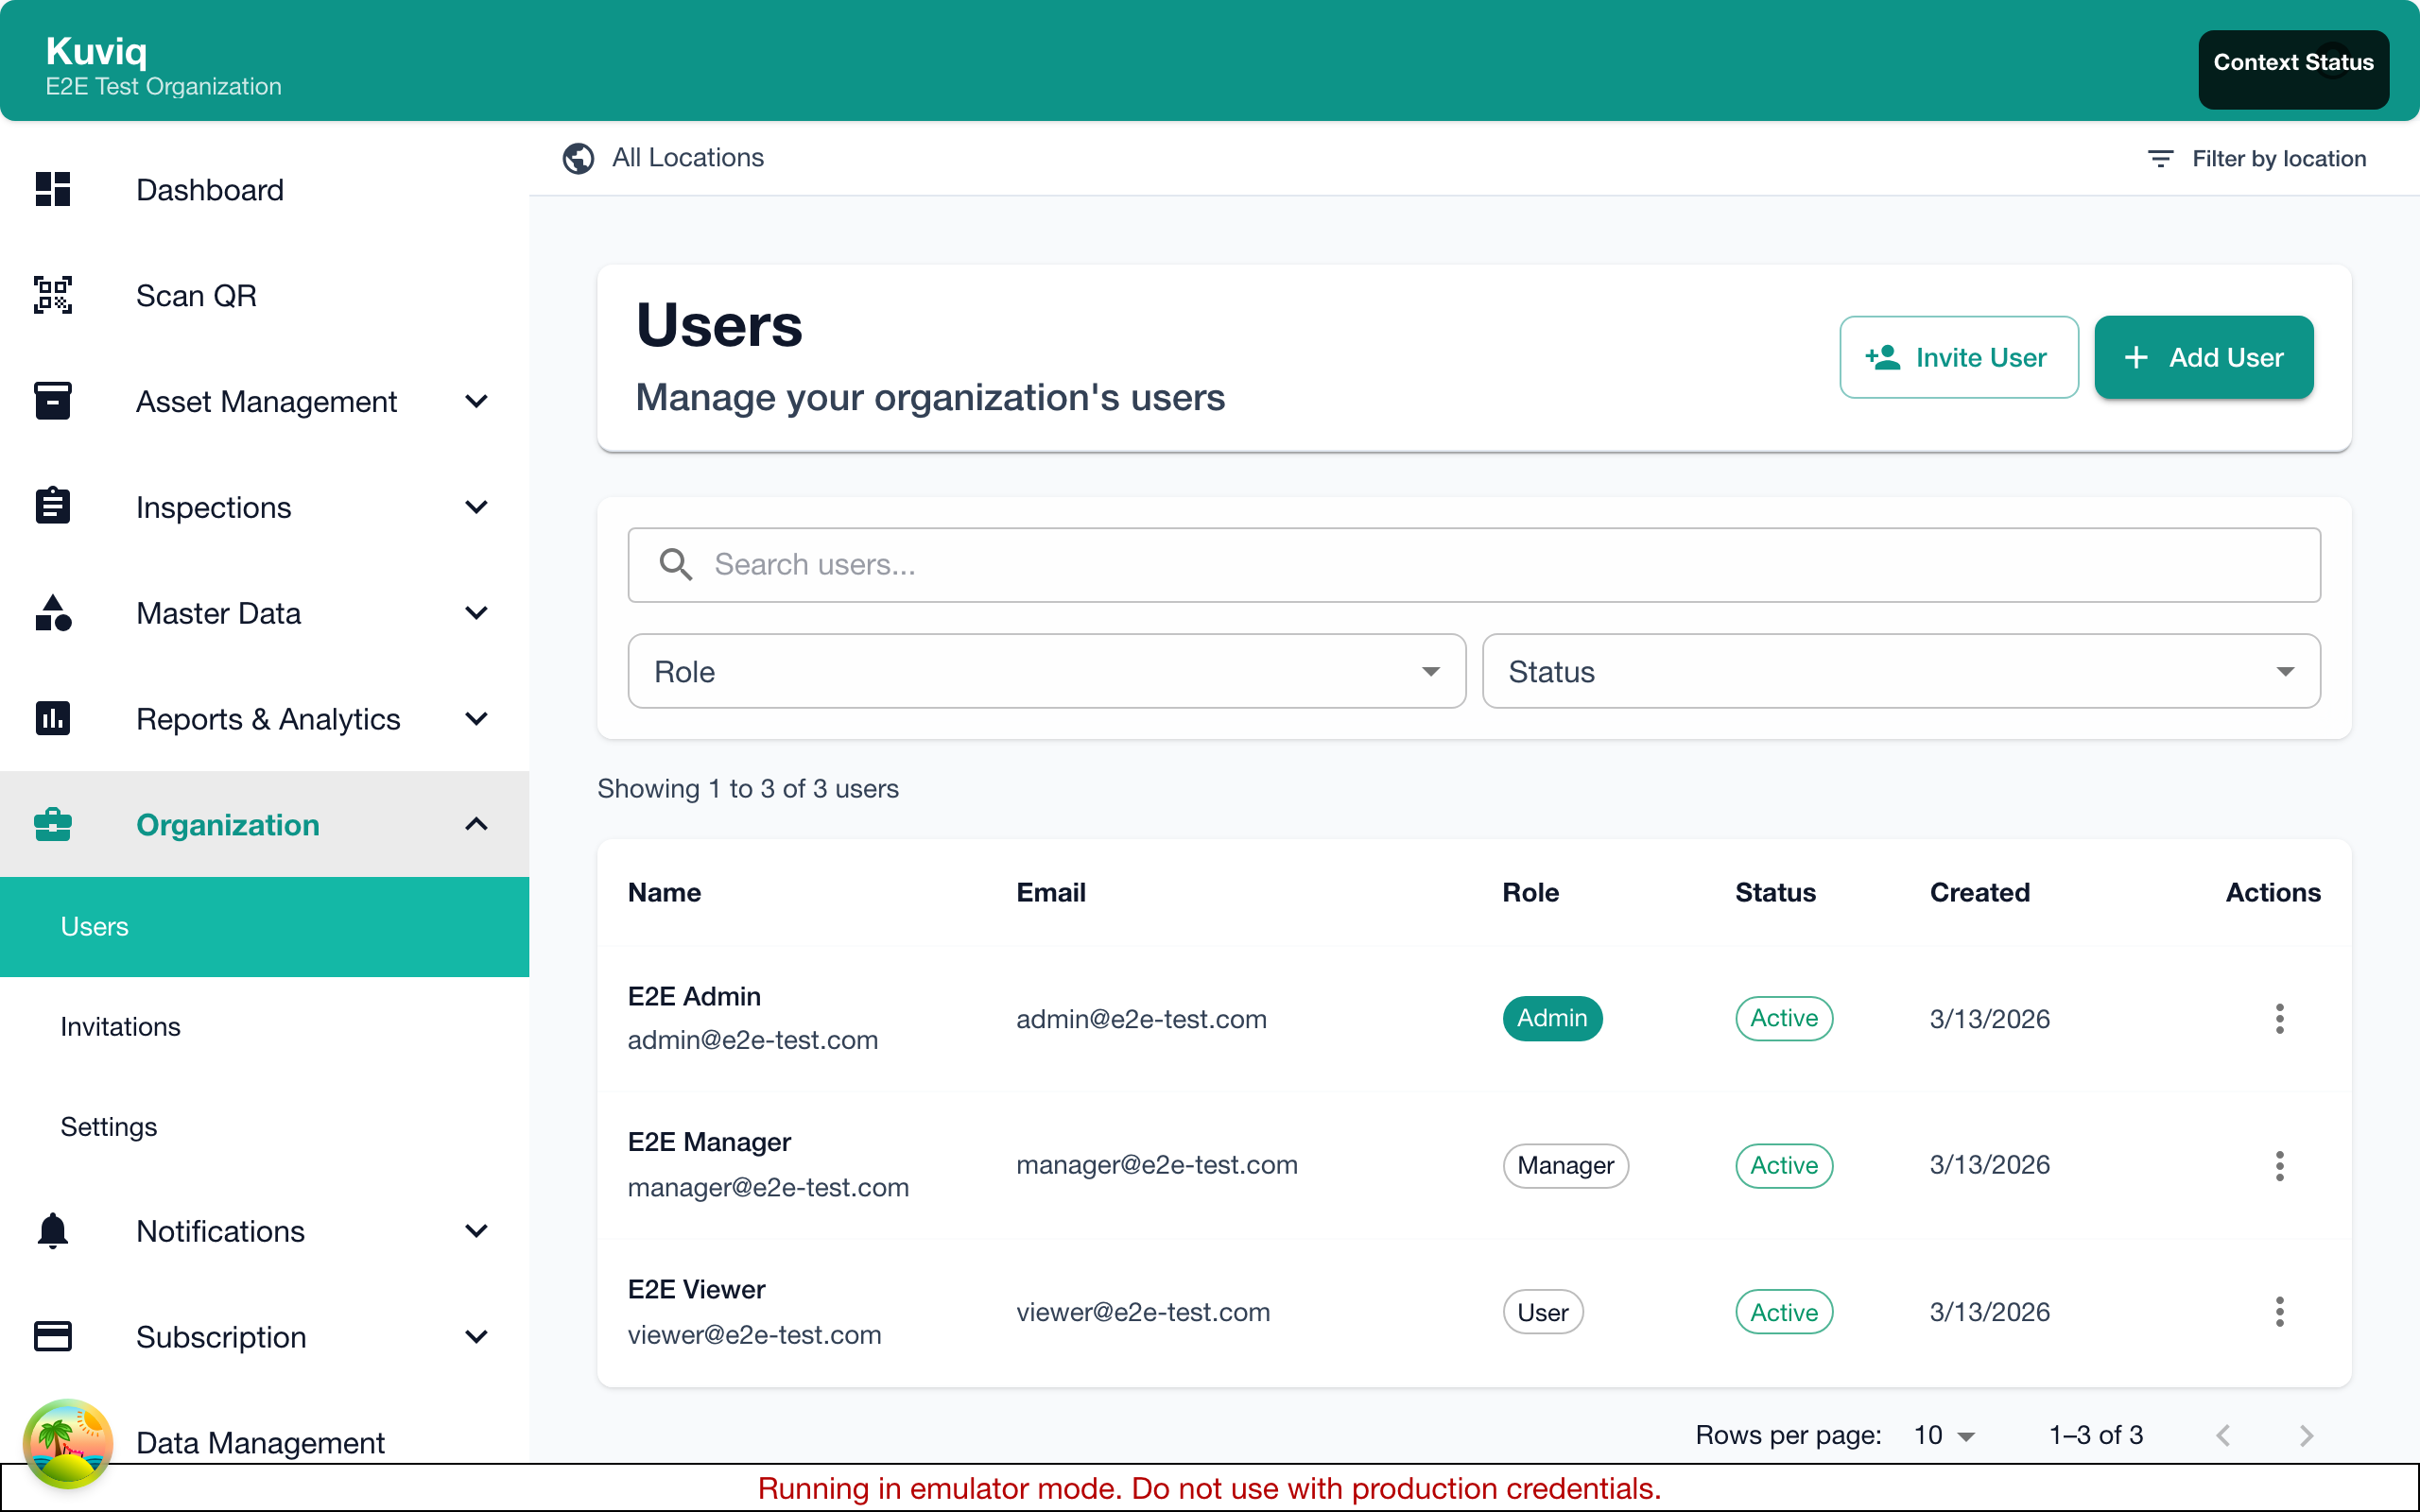
Kuviq uses roles to define what users can access and do. Each role has a specific purpose and set of permissions.
Available Roles
| Role | Purpose |
|---|
| Super Admin | Complete system control including billing |
| Admin | Full operational access without billing |
| Manager | Operational management and oversight |
| User | Day-to-day inspection and basic access |
Super Admin
Purpose
The Super Admin has complete control over the organization, including sensitive operations like billing and data management.
Capabilities
| Area | Can Do |
|---|
| Users | Create, edit, delete all users including admins |
| Items | Full control over all items |
| Inspections | Full control over all inspections |
| Configuration | All settings and templates |
| Billing | Manage subscription, payments, invoices |
| Data | Export, delete, archive organization data |
| Security | Audit logs, security settings |
Who Should Have This Role
- Organization owner
- IT administrator
- Financial controller
- 1-2 people maximum recommended
Limitations
- Cannot be demoted by regular Admins
- Must have at least one Super Admin
- Self-demotion requires another Super Admin
Admin
Purpose
Admins manage day-to-day operations and user administration without access to billing.
Capabilities
| Area | Can Do |
|---|
| Users | Create, edit, delete users (not Super Admins) |
| Items | Full control over all items |
| Inspections | Full control over all inspections |
| Configuration | Modify all settings and templates |
| Reports | Generate all reports |
| Locations | Manage all locations |
What Admins Cannot Do
- Access billing and subscription
- Manage Super Admin accounts
- Delete organization
- View financial data
Who Should Have This Role
- Department managers
- Safety managers
- Operations managers
- Team leads with admin responsibilities
Manager
Purpose
Managers oversee operations without making configuration changes.
Capabilities
| Area | Can Do |
|---|
| Users | View users in their scope |
| Items | Create, edit, view all items |
| Inspections | Create, edit, view all inspections |
| Reports | Generate operational reports |
| Locations | View all locations |
What Managers Cannot Do
- Create or edit users
- Modify configuration (templates, item types)
- Delete items or inspections
- Change organization settings
Who Should Have This Role
- Shift supervisors
- Site managers
- Department leads
- Quality managers
User
Purpose
Users perform day-to-day inspection tasks and basic operations.
Capabilities
| Area | Can Do |
|---|
| Items | View assigned/accessible items |
| Inspections | Perform inspections, view own history |
| QR Codes | Scan QR codes |
| Profile | Edit own profile |
What Users Cannot Do
- Manage other users
- Delete items
- Configure system
- Access admin features
- Generate advanced reports
Who Should Have This Role
- Inspectors
- Technicians
- Field workers
- General staff
Role Comparison Matrix
Item Permissions
| Action | Super Admin | Admin | Manager | User |
|---|
| View all items | ✓ | ✓ | ✓ | Limited |
| Create items | ✓ | ✓ | ✓ | ✓ |
| Edit items | ✓ | ✓ | ✓ | Own |
| Delete items | ✓ | ✓ | - | - |
| Export items | ✓ | ✓ | ✓ | - |
Inspection Permissions
| Action | Super Admin | Admin | Manager | User |
|---|
| View all | ✓ | ✓ | ✓ | Own |
| Perform | ✓ | ✓ | ✓ | ✓ |
| Edit | ✓ | ✓ | ✓ | Own |
| Delete | ✓ | ✓ | - | - |
| Export | ✓ | ✓ | ✓ | - |
User Management
| Action | Super Admin | Admin | Manager | User |
|---|
| Invite users | ✓ | ✓ | - | - |
| Edit users | ✓ | ✓ | - | Own |
| Delete users | ✓ | ✓ | - | - |
| Change roles | ✓ | Limited | - | - |
Configuration
| Action | Super Admin | Admin | Manager | User |
|---|
| Item types | ✓ | ✓ | View | View |
| Templates | ✓ | ✓ | View | View |
| Locations | ✓ | ✓ | View | View |
| Settings | ✓ | ✓ | - | - |
Billing
| Action | Super Admin | Admin | Manager | User |
|---|
| View billing | ✓ | - | - | - |
| Change plan | ✓ | - | - | - |
| View invoices | ✓ | - | - | - |
| Update payment | ✓ | - | - | - |
Assigning Roles
During Invitation
- Go to Admin > Users
- Click Invite User
- Enter email
- Select role
- Send invitation
Changing an Existing User's Role
- Go to Admin > Users
- Click on the user
- Click Edit
- Change the role
- Save
Restrictions
- Cannot change your own role
- Admins cannot create Super Admins
- Admins cannot demote Super Admins
- Must have at least one Super Admin
Role Recommendations
Small Teams (2-10 people)
| Team Size | Recommended Roles |
|---|
| 2-3 | 1 Super Admin, rest Users |
| 4-6 | 1 Super Admin, 1 Admin, rest Users |
| 7-10 | 1 Super Admin, 1-2 Admins, 1-2 Managers, rest Users |
Medium Teams (10-50 people)
| People | Recommended |
|---|
| 1-2 | Super Admin |
| 2-5 | Admin |
| 5-10 | Manager |
| Rest | User |
Large Organizations (50+)
| Role | Number |
|---|
| Super Admin | 1-2 |
| Admin | Per department |
| Manager | Per team/location |
| User | All others |
Common Scenarios
Single Person Organization
- Assign yourself Super Admin
- Full control as the only user
Small Business
| Role | Who |
|---|
| Super Admin | Owner |
| User | Staff |
Multi-Site Operation
| Role | Who |
|---|
| Super Admin | Corporate admin |
| Admin | Regional managers |
| Manager | Site supervisors |
| User | Inspectors |
Compliance-Focused
| Role | Who |
|---|
| Super Admin | Compliance officer |
| Admin | Quality managers |
| Manager | Team leads |
| User | Inspectors |
Best Practices
Principle of Least Privilege
Give users only the access they need:
- Start with User role
- Upgrade only if needed
- Document why higher access is needed
Regular Reviews
Periodically review role assignments:
- Who has Admin/Super Admin?
- Are roles still appropriate?
- Any role changes needed?
Avoid These Mistakes
- Too many Super Admins - Increases risk
- Everyone as Admin - Defeats purpose of roles
- Not using Manager - Missing middle tier
- Not documenting - Forget why someone has access
Troubleshooting
User Can't Access Feature
- Check their role
- Review role permissions
- Consider if they need a higher role
- Or use location-based access instead
Wrong Role Assigned
- Edit the user
- Change their role
- Have them refresh browser
Can't Demote Super Admin
- Another Super Admin must do it
- Ensure at least one Super Admin remains
Next Steps